New iPhone Exploit is Crazy #cyber #hacking #iphone #jailbreak
3-Second Blueprint (English)
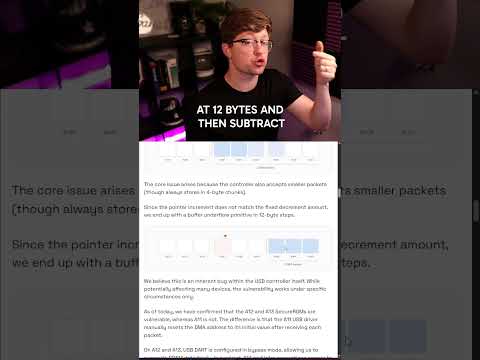
- The unpatchable usbliter8 hardware vulnerability exploits USB packet pointer arithmetic in Apple SoC BootROM during DFU mode.
- Sending three 4-byte USB packets instead of 8-byte packets advances a pointer 12 bytes then subtracts 24, causing a buffer underflow.
- With physical USB access in DFU mode, the underflow overwrites the USB controller task's return address to bypass Secure Boot.
usbliter8 BootROM ExploitBuffer UnderflowUSB Packet Pointer ArithmeticReturn Address OverwriteDFU Mode & Secure Boot
3-Sekunden-Fazit (Deutsch)
- Die nicht per Update behebbare Hardware-Lücke usbliter8 nutzt fehlerhafte USB-Zeigerarithmetik im Apple-BootROM im DFU-Modus aus.
- Drei 4-Byte- statt 8-Byte-Pakete schieben den Zeiger um 12 Bytes vor und ziehen 24 ab, was einen Buffer-Underflow auslöst.
- Mit physischem USB-Zugriff im DFU-Modus überschreibt dies die Rücksprungadresse des USB-Tasks und umgeht Secure Boot.
usbliter8-BootROM-ExploitBuffer-UnderflowUSB-ZeigerarithmetikRücksprungadressen-ÜberschreibungDFU-Modus & Secure Boot
Note / Hinweis: Blueprints are AI-generated educational summaries (0% Politics · 0% Religion · 0% Brainrot) and do not constitute medical, legal, or financial advice. / KI-generierte Zusammenfassung zu Bildungszwecken – ersetzt keine medizinische, rechtliche oder finanzielle Fachberatung.